Web Development
 Data Science
 Python
 SQL
 JavaScript
 Artificial Intelligence
 IT & Software
 IT Certifications
 Hacking
 AWS
 Arduino
 DevOps
 3D Modeling
 Graphic Design
 Photoshop
 Drawing
 Digital Painting
 UX Design
 Business
 Data Analysis
 Communication Skills
 Project Management
 Leadership & Management
 Human Resources
 Digital Marketing
 Social Media Marketing
 Marketing
 SEO
 Google Analytics
 Branding
 Excel
 Office Productivity
 SAP
 PowerPoint
 Microsoft Access
 SharePoint
 Finance & Accounting
 Trading & Investing
 Accounting
 Bitcoin
 Personal Finance
 Video Editing & Animation
 Photography
 Adobe Premier Pro
 Adobe Lightroom
 Personal Development
 Productivity
 Career Development
 Life Coaching
 Health & Fitness
 Meditation & Mindfulness
 Yoga
 Music
 Music Production
 Guitar
 Piano
 Singing
 Language Learning
 Teaching & Academics
 Engineering
 Math
 Lifestyle
 Rajganesh Pandurangan Courses
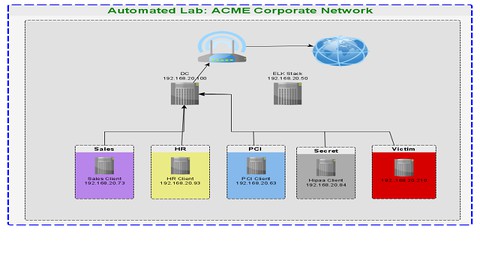
How to automate active directory labs for pentesting
4.5 (2,016 Reviews)
 Provider: Udemy
 Time: 4.4h
- 2021
$69.99
Visit Most Recent Review
awesome practical implementation to each piece of information, you're really appreciated. every review my knowledge being leveraged and my technical experience has enhanced. hoping you the best ever, looking for more tutorials to deepen my knowledge, experience and hence joining a reputable organization as Dell, HP, Google to prove my identity and technical skills.
- Review by Peter Youssef Gabra on How to automate active directory labs for pentesting
 Instructor Bio
Hello All
I'm a security expert with over two decades of security consulting experience. Some of my skills are listed below:
Windows Security Expert – Both offensive and defensive techniques
Performed Network pentesting, security code reviews and application risk assessments for customer facing applications at Fortune 100 companies.
Lead and manage security consultants at U.S.Bank to improve security posture of applications, networks, and Mobile applications.
Delivered several million dollars of security services and technology for clients in the financial, retail, healthcare, manufacturing, and utilities sectors.
Performed Red team hacking for many Fortune 500 companies
Introduced security risk assessments and threat modeling techniques into the organization.
Acted as technical authority on security for numerous RFPs and during contract negotiations.
Participated in many PCI Assessments for many small, large and multinational companies and performed gap analysis, consultation, and development of customized solutions.
Audited applications written in multiple languages, including Java/JSP, VB.NET, ASP.NET, C#, C/C++, PHP.
Web Penetration testing to prove Software Security Vulnerabilities with IBM AppScan, Burp Professional, Paros and Manual Fuzzing and Penetration Testing with AppScan and Firefox plug-ins.
Trained, documented and advised application developers in regards to security risks, secure coding best practices, with practical remediation guidance provided to developers.
Drove the adoption of security scanning tools for both development and production use. Tools utilized: Qualys and IBM Rational AppScan.
Trained developers to write secure code using the OWASP software security testing guide.
Found Software security vulnerabilities for clients including: SQL injection, XSS, Cross Site Request Forgery and multiple other vulnerabilities.
Tested many networks and over a thousand Fortune 100 web applications for security issues; tested top company external and internal and penetrated into systems.
Professional Certifications
Offensive Security Certified Professional (OSCP)
Cisco Certified Network Associate (CCNA)
GIAC GSSP-JAVA Certification
Certified Ethical Hacker (CEH)
Certified Information Systems Security Professional (CISSP)