
 Web Development
 Data Science
 Python
 SQL
 JavaScript
 Artificial Intelligence
 IT & Software
 IT Certifications
 Hacking
 AWS
 Arduino
 DevOps
 3D Modeling
 Graphic Design
 Photoshop
 Drawing
 Digital Painting
 UX Design
 Business
 Data Analysis
 Communication Skills
 Project Management
 Leadership & Management
 Human Resources
 Digital Marketing
 Social Media Marketing
 Marketing
 SEO
 Google Analytics
 Branding
 Excel
 Office Productivity
 SAP
 PowerPoint
 Microsoft Access
 SharePoint
 Finance & Accounting
 Trading & Investing
 Accounting
 Bitcoin
 Personal Finance
 Video Editing & Animation
 Photography
 Adobe Premier Pro
 Adobe Lightroom
 Personal Development
 Productivity
 Career Development
 Life Coaching
 Health & Fitness
 Meditation & Mindfulness
 Yoga
 Music
 Music Production
 Guitar
 Piano
 Singing
 Language Learning
 Teaching & Academics
 Engineering
 Math
 Lifestyle
Secure Programming of Web Applications - Developers and TPMs (Udemy.com)
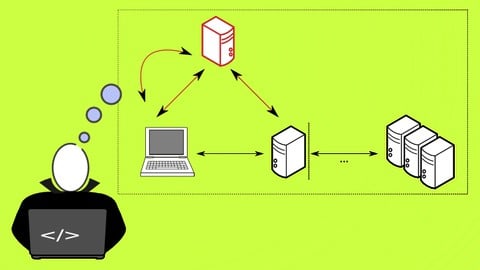
Web Application Security for Software Developers and Technical Project Managers
Created by: Frank Hissen
Last updated August 2026
 What you will learn
- Security of Web Applications
- Secure Programming Patterns
- Security Baselines
- Secure Coding
How it compares
Against the other 523 rated Udemy courses in Hacking on CourseDuck:
- Rating4.5 out of 5higher than 51% of them
- Reviews7,031#26 of 524 by number of reviews
- Length1.9 hoursshorter than 84% of them
- Last updatedAugust 2026more recently than 84% of them
 Course Description
Understand Application Security: Numerous successful attacks on well-known web applications on a weekly basis should be reason enough to study the background of "Web Application Security" of custom-made or self-developed applications.
Computer systems are ubiquitous and part of our working and private everyday life. For companies it is increasingly complex and difficult to keep up their IT security with the current technical progress. Large enterprises establish security processes which are created according to industry standards (e.g., ISO 27001). These processes are very complex and can only be implemented by teams of security experts. Constant quality assurance, maintenance and adaptation also belong to an IT security process.
It does not matter if a company develops products or runs an online shop, IT security is a characteristic feature. Security incidents, which maybe even reach public uncontrolled, do not only damage the business image but may also lead to legal or financial consequences.
Intro
Typical Vulnerabilities Overview
Cause & Background
Secure Programming in general
Code/Command Injection in general
(No)SQL Code Injection
Cross-Site Request Forgery (CSRF)
Cross-Site Scripting (XSS)
Open Redirection
File Inclusion / Directory Traversal
Clickjacking
Session-Hijacking
Information Disclosure
Attacks on Weaknesses of the Authentication
Denial of Service
Middleware
Third-Party Software
Summary and Conclusion
The principles taught in this course are language and platform independent. However, the course will include examples for Java and PHP.
Instructor Frank Hissen, Computer Scientist and Security Expert, teaches IT security for over 20 years and works for companies of all sizes as IT Security Consultant and Software Engineer.

 Udemy Discount
The discount is applied through our link. Open the course from here and Udemy's current promotional price is applied at checkout on most courses, no code to type.
Some courses are excluded from Udemy's promotions. If the price does not drop, clear your browser cookies and use the button again.
Instructor Details
- 4.5 Rating
 7,031 Reviews
Frank Hissen
Frank Hissen successfully studied Computer Science at Darmstadt University of Technology (Germany) focusing on IT security. For over 25 years, he works as IT consultant and software engineer; for over 20 years, he also works in various positions as security expert in IT development and consulting projects of large businesses but also medium-sized companies.
In the area of IT security, Mr. Hissen is specialized in applied and technical IT security. He developed and implemented security solutions and accompanied processes for secure product and software development.
In the area of cryptography and encryption, Mr. Hissen developed security solutions as Senior Solution Engineer at SECUDE before he became self-employed in 2009. Since then he works as freelancing expert in the area of web and cloud application security. He creates secure conceptual designs of system architectures but also takes care of their secure implementation and corresponding security requirements.
Mr. Hissen worked in various projects among others for Deutsche Telekom AG, SECUDE, Allianz AG and SAP Research.
 More Hacking courses

Getting Started with Wireshark: The Ultimate Hands-On Course (2025)
4.8 (12,167 Reviews)
 Provider: Udemy
 Time: 4.4h
$109.99

The Ultimate Dark Web, Anonymity, Privacy & Security Course (2025)
4.8 (9,329 Reviews)
- Provider: Udemy
- Time: 10.3h
$27.99

Computer Basics for Beginners: Understanding Computer Basics (2025)
4.8 (4,524 Reviews)
- Provider: Udemy
- Time: 5.8h
$14.99

Ultimate F5 LTM Training from Beginner to Expert 2026
4.8 (1,927 Reviews)
- Provider: Udemy
- Time: 13.5h
$84.99

IP Addressing and Subnetting - Hands-on Learning Approach (2020)
4.8 (1,522 Reviews)
- Provider: Udemy
- Time: 4.2h
$15.99

Cisco BGP Masterclass for Enterprise Network Engineers (2026)
4.8 (1,369 Reviews)
- Provider: Udemy
- Time: 16.4h
$11.99
 Reviews

By Patrick Ashburn on 6/30/2026
Useful information covering real-world examples, many of which I have encountered on projects over the years. Well-organized and succinctly presented. Definitely worth the time and worth revisiting as a valuable resource.
By Lucas Anderson on 6/11/2026
Gostei bastante, bem informativo
By Micheal Padden on 3/31/2026
Good run through. Well structured, clear recommendations. Good examples, easy to follow.
By Derek Oppenheimer on 10/3/2025
I had difficulty conceptualizing some of the attacks until the demo's so those were great!
By Clayton Wardell on 3/20/2025
He is very good at delivering the content, he knows the subject matter. Obviously English is not his first language, and there are some grammatical errors, in the text. Also I would like to have seen a few more examples during the lectures.
By Christian on 9/26/2024
Good quick course that covers the most common things in web. I'll just leave some feedback if the speaker wants to improve the course: -When talking about authentication/passwords I saw two mistakes: OTP dosen't mean "One time password", it means "One time pad", it only means password in the context of TOTP or HOTP. The other one is the recommendation of password length of 8, that can be bruteforced in less than an hour, you should recommend a bigger number like 12. -For the exam, some things are not explained on the course itself or are ambiguous, I could do it no problem because I work in security and I know the answers anyway (and they are true), but the people target of the course can have problems with that even if they did it paying attention. Let me give you an example: In the question about "secure against brute force", you only talked about bruteforcing against the login, that is why you recommended blocking accounts. In that context, only iterations and another option are relevant (iterations because they slow down each attempt), but you marked also the algorithm itself and salt as options. They are TRUE but ONLY if you also take into account brute forcing the HASH, salt has no impact while bruteforcing words in a login, and same for the algorithm itself. That was never mentioned during the course.
By Anonymized User on 7/10/2024
The content on this training was great, but the plainness of the slides made just listening to it kind of dull. I liked the section on CSRF and session hijacking. I wish it included a bit more beyond just examples, like if REST APIs are vulnerable to CSRF. I like that it was only 1.5 hours, that is a lot of content for a short period.
By Erik Szabo on 3/27/2024
Very good entry-level course into the topic. Sometimes the summaries are rather dense and there is little space to practice, but if you need a compact introduction, it's exactly what you get here. For me it was great to identify those areas where I will be interested in finding more detail in dedicated resources.
By Asif Iqbal on 5/10/2023
It was basic coruse but provided some basic information and that a developer should keep in mind while making comples applications.
By Oyetunde Faniran on 7/4/2021
The instructor was able to pass the knowledge in simple terms. Though it feels as if one is just viewing a drabby Powerpoint presentation on a white background, but he made his point known nonetheless. Inclusion of quizzes would also help to confirm that the student understands what is being taught. Though, all in all, it's still a good one.
 Quality Score
No CourseDuck member has rated this course yet. Taken it? Give each part a thumbs up or down.
Overall Score : 90 / 100
- Video Duration:
 1.9h
- Price: $44.99
- Provider: Udemy
- Updated:
 August 2026
- Level:
 Intermediate
- Language:
 English
- Certificate:
 Yes
30-day money-back guarantee on most paid courses
Udemy Coupon Price Tracker
