
 Web Development
 Data Science
 Python
 SQL
 JavaScript
 Artificial Intelligence
 IT & Software
 IT Certifications
 Hacking
 AWS
 Arduino
 DevOps
 3D Modeling
 Graphic Design
 Photoshop
 Drawing
 Digital Painting
 UX Design
 Business
 Data Analysis
 Communication Skills
 Project Management
 Leadership & Management
 Human Resources
 Digital Marketing
 Social Media Marketing
 Marketing
 SEO
 Google Analytics
 Branding
 Excel
 Office Productivity
 SAP
 PowerPoint
 Microsoft Access
 SharePoint
 Finance & Accounting
 Trading & Investing
 Accounting
 Bitcoin
 Personal Finance
 Video Editing & Animation
 Photography
 Adobe Premier Pro
 Adobe Lightroom
 Personal Development
 Productivity
 Career Development
 Life Coaching
 Health & Fitness
 Meditation & Mindfulness
 Yoga
 Music
 Music Production
 Guitar
 Piano
 Singing
 Language Learning
 Teaching & Academics
 Engineering
 Math
 Lifestyle
Learn Step by Step Web Hacking and Penetration Testing (Udemy.com)
You will learn hacking tools, methodologies and techniques and and learn how to secure them from these hackers.
Created by: Gabriel Avramescu
Last updated December 2019
 What you will learn
- Understand and perform the basic steps in order to performa penetration testing of a web application
- Understand web application's security principles and potential dangers
- Be able to gather information about your target
- You will learn how to find vulnerabilities in your target web application
- Exploit found vulnerabilities and get control over remote servers
- Understand the penetration testing process
- As a web application developer you will understand how to secure your application
How it compares
Against the other 523 rated Udemy courses in Hacking on CourseDuck:
- Rating4.7 out of 5higher than 85% of them
- Reviews823#209 of 524 by number of reviews
- Length9.4 hourslonger than 69% of them
- Last updatedDecember 2019earlier than 86% of them
 Course Description
In order to protect yourself from hackers, you must think as one.
This training is based on a practical approach of day-by-day situations and it contain labs based on real environments.
In this course, you will start as a beginner with no previous knowledge about penetration testing or hacking.
This course is focused on the practical side of penetration testing without neglecting the theory behind each attack. Before jumping into penetration testing, you will first learn how to set up a lab and install needed software to practice penetration testing on your own machine.
The course objective is to help you learn to master the (ethical) hacking techniques and methodology that are used in penetration systems. The course is designed for IT passionate, network and system engineers, security officers.
Once you understand how websites work we will start talking about how can we exploit these components. This course will take you from a beginner to a more advanced level -- so you will be able to launch attacks and test the security of websites and web applications, and furthermore you'll be able to help fixing these vulnerabilities and secure websites from them.
Below are the main topics, both theoretical and practical, of this course:
Core problems (Causes. Defences)
Web Technologies (HTTP Protocol, Web Functionality, Encoding)
Mapping (Spidering and Analysing)
Attacking Authentication (Technologies, Flaws, Fixes, Brute Force)
Attacking Session Management (State, Tokens, Flaws)
Attacking Access Controls (Common Vulnerabilities, Attacks)
Attacking Data Stores (SQL Injection, Bypassing Filters, Escalation)
Bypassing Client-Side Controls (Browser Interception, HTML interception, Fixes)
Attacking the server (OS command Injection, Path Traversal, Mail Injection, File Upload)
Attacking Application Logic
Cross Site Scripting
Attacking Users (CSRF, ClickJacking, HTML Injection)
OWASP Top Ten Vulnerabilities
Network Attacks
Labs:
Spidering, Website Analyser
Brute-Force
Session Hijacking via Mann-in-The-Middle
Get Gmail or Facebook Passwords via SSLStrip
SQL Injection
Upload File and Remote Execution
Cross-Site Scripting (Stored + Reflected, Cookie Stealing, Preventing XSS)
CSRF (Change password trough CSRF vuln., Preventing CSRF)
NOTE: This course is created only for educational purposes and all the attacks are launched in an isolated lab environment.

 Udemy Discount
The discount is applied through our link. Open the course from here and Udemy's current promotional price is applied at checkout on most courses, no code to type.
Some courses are excluded from Udemy's promotions. If the price does not drop, clear your browser cookies and use the button again.
Instructor Details
- 4.7 Rating
 823 Reviews
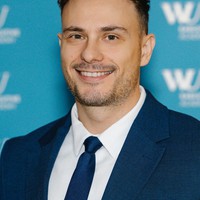
Gabriel Avramescu
Senior Information Security Consultant
- I work in the Internet security team, focused on ethical hacking - deliberately and purposefully challenging the IT security assumptions, strategies, and methods of protecting vital assets and information by emulating an adversary.
- Scan and exploit for a wide variety of data center infrastructure and application vulnerabilities, following defined rules of engagement and attack scenarios (ethical hacking).
- Make recommendations on security weaknesses and report on activities and findings.
- Perform Internet penetration testing (black box / white box testing) and code reviews (manual and automated)
- Use testing tools as NetBIOS scanning, network pinging and testing, packet crafting and analyzing, port scanning for vulnerability assessment
- Perform analysis and testing to verify the strengths and weaknesses of Web Applications and Web Services (SML, SOAP, WSDL, UDDI, etc.)
- Perform analysis and testing to verify the strengths and weaknesses of a variety of operating systems, network devices, web applications, and security architectures
- Assist with the development of remediation services for identified findings
- Customize, operate, audit, and maintain security related tools and applications
IT Trainer
- CEH, ECSA, CHFI, ECIH, ICS-SCADA Cybersecurity from EC-Council
 More courses by Gabriel Avramescu
Mobile Penetration Testing of Android Applications (2024)
4.6 (2,909 Reviews)
 Provider: Udemy
 Time: 6h
$16.99
Offensive Perspective - OWASP Security for Developers (2026)
4.8 (785 Reviews)
- Provider: Udemy
- Time: 4.5h
$74.99
Build up on VMware vSphere & ESXi in Enterprise Environmmet (2021)
4.7 (479 Reviews)
- Provider: Udemy
- Time: 2.3h
$12.99
More Hacking courses

Getting Started with Wireshark: The Ultimate Hands-On Course (2025)
4.8 (12,167 Reviews)
- Provider: Udemy
- Time: 4.4h
$109.99

The Ultimate Dark Web, Anonymity, Privacy & Security Course (2025)
4.8 (9,329 Reviews)
- Provider: Udemy
- Time: 10.3h
$27.99

Computer Basics for Beginners: Understanding Computer Basics (2025)
4.8 (4,524 Reviews)
- Provider: Udemy
- Time: 5.8h
$14.99

Ultimate F5 LTM Training from Beginner to Expert 2026
4.8 (1,927 Reviews)
- Provider: Udemy
- Time: 13.5h
$84.99

IP Addressing and Subnetting - Hands-on Learning Approach (2020)
4.8 (1,522 Reviews)
- Provider: Udemy
- Time: 4.2h
$15.99

Cisco BGP Masterclass for Enterprise Network Engineers (2026)
4.8 (1,369 Reviews)
- Provider: Udemy
- Time: 16.4h
$11.99
 Reviews

By Kaizan Irani on 6/8/2025
This course is pretty old. Last updated in 2019. Technology changes by the minute. The tutor has not updated his course accordingly. I would love to see a 2025 based fully refreshed course by him.
By Delo Cannondale on 10/31/2023
I have already learned the basics of hacking and was looking to get more into depth to technical side of things, this course really helped with that.
By Sally Harper on 10/20/2023
Sounds excellent thus far. I already have the impression that it will be a wonderful setting with wonderful people where I may learn.
By Jesse Hill on 7/31/2023
This was quite satisfying for me because I had always longed for an education that was full of detailed explanation and example. I want to work professionally in the security industry because I'm quite interested in it.
By Marc Hill on 3/17/2018
Absolutely outstanding content and logical progression, I have taken a lot of notes and have managed to get a much greater understanding of pen-testing. I do find Gabriel much easier to understand by speeding the videos up slightly.
By Costin Saftu on 2/7/2017
interesting course! Always wanted to learn ethical hacking so the lessons offer important knowledge to me. For the start, I like the course.
By Ajay S on 1/19/2017
Just the course I have been looking for. Something that will start from installing a web server, running a web application and then going about discovering and exploiting specific vulnerabilities and then learn how to plug these risks. Great course!
By Kashif on 4/19/2016
The course provides a good starting point for beginners. You can consider it as beginning of a new journey and the subject does require tremendous amount of reading and practising along with what has been offered in the course. What I truly appreciate is the instructors command over the subject, promptness in answering the questions and doing so with passion and sincerity. I am learning a lot by posing to-the-point questions and Gabriel has never disappointed me. I am more than happy to recommend it to any potential learners. Thank you so much Gabriel, you have truly been a great help.
By Arnold Daniels on 4/4/2016
You look over the shoulder of a penetration tester while he goes through the steps. You see him making small mistakes like typos. All-in-all it feels pretty rough and a bit under-prepared. That said, I did take away quite a bit of useful information about penetration testing from this course. So I don't regret taking this course.
By John B Higgins on 3/6/2016
I would be very excited to possibly working from home and getting paid.This course is laid out very well to allow concentrated thinking.
 Quality Score
No CourseDuck member has rated this course yet. Taken it? Give each part a thumbs up or down.
Overall Score : 94 / 100
- Video Duration:
 9.4h
- Price: $16.99
- Provider: Udemy
- Updated:
 December 2019
- Level:
 All Levels
- Language:
 English
- Certificate:
 Yes
30-day money-back guarantee on most paid courses
Udemy Coupon Price Tracker
